P
Protection Core
ACTIVEOwner and managed-user enforcement is active.
Security controlOpen control →
WordPress security built for ownership
CR Guard is a WordPress application-security control plane for identity, API access, malware integrity, pre-execution trust, persistence defense and incident response.
Security overview
example.com · just now
Access risk
Low
Files checked
31,420
All matched
Active users
04
Monitored
Protection layers
View activity
Access policies enforced
Protection at a glance
System baseline
Ready & monitored
9
Security layers
One unified control plane
SHA-256
File integrity
Trusted verification baseline
Blocked
Remote mutations
Sensitive changes restricted
Full
Incident context
Evidence & recovery visibility
CR Guard brings identity, access, execution, integrity and incident controls into one security model, giving you a clear view of the protection layers active across your WordPress environment.
9
Security layers
100%
Recommended controls
24/7
Monitoring
Security pulse
Activity across your protected WordPress environment
23
Blocked events
Security & policy blocks
22
Failed logins
Authentication failures
0
Suspicious requests
Payload / upload signals
1
API / state blocks
Remote mutations stopped
0
File changes
FIM changes detected
2
Critical findings
Current security findings
0
Admin changes
Privilege / identity events
18
Integrity drift
Current integrity findings
Monitor the controls that matter most and quickly identify where attention is required.
Owner and managed-user enforcement is active.
Deterministic early CR Guard loader is installed and valid.
Rapid integrity monitoring is active.
2 critical current findings require review.
Persistence indicators are monitored across the installation.
Sensitive remote mutations are blocked by policy.
Plugin and extension access is restricted.
Administrator activity is continuously tracked.
Evidence and recovery workflows are available.
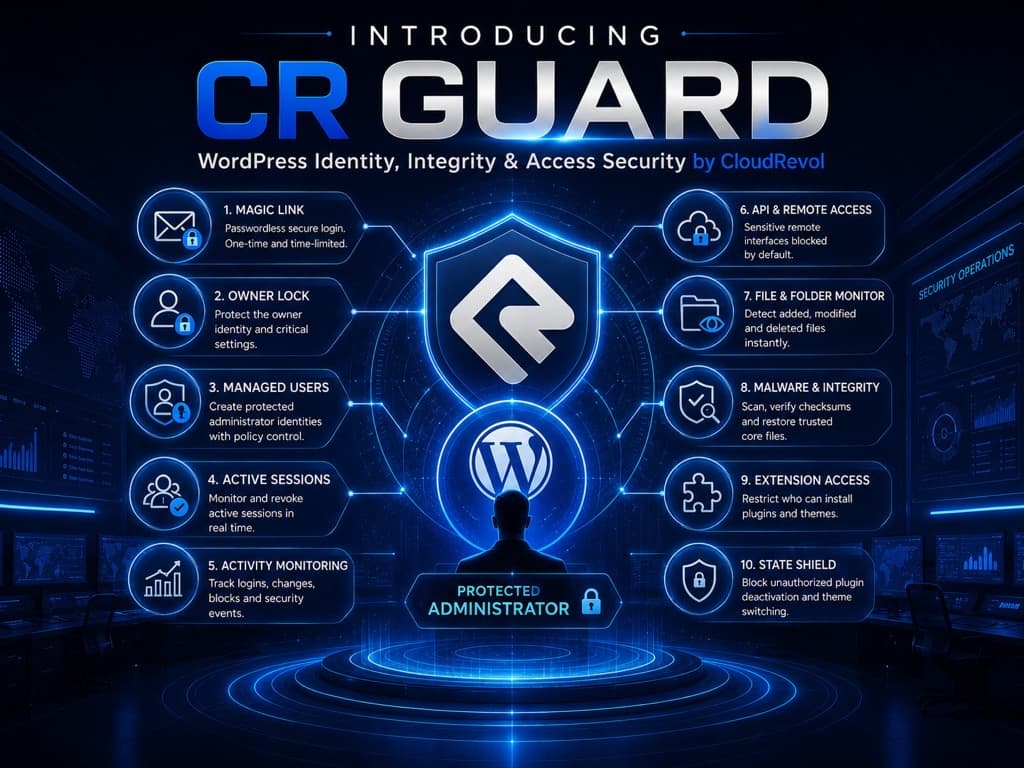
CR Guard adds an advanced security layer to WordPress, protecting administrator identity, authentication, sessions, APIs, files and sensitive changes from one controlled security model.
CR Guard gives you a centralized Incident Center where you can monitor, prioritize, and investigate security events across your WordPress environment before they become bigger problems.
Quickly identify critical, high, medium, and operational events that require attention.
Malware, integrity, injection, persistence, file monitoring, API, and authentication events are brought together.
Review the affected asset, source, severity, and evidence before taking containment or recovery actions.
One prioritized investigation queue across your security events.
A layered security model designed to control identity, access, execution, integrity and response across your WordPress environment.
Sign in with a short-lived magic link sent to verified CloudRevol identities.
Protect your WordPress site against malware, injections, unauthorized changes, backdoors and other common security threats.
Protect APIs, remote access channels and external integrations from unauthorized requests, abuse and malicious state changes.
Protect the site owner, key settings and administrator authority from unauthorized changes.
Create and approve team access from one controlled, auditable workflow.
Review active sessions, revoke suspicious access and restrict who can install or upload extensions.
Continuously scan for malware, file tampering, injected code and unexpected changes across your WordPress installation.
Customize your WordPress experience with your own logo, colors and visual identity.
Track important site and administrative changes with a clear history of actions, users and timestamps.
Detect malicious code injections, hidden backdoors and unauthorized changes designed to maintain persistent access.
Detect additions, modifications and removals across your WordPress install.
Compare trusted WordPress core and extension files to spot unexpected change.
Prioritize evidence, preserve context, revoke sessions and move through a controlled recovery path.
Safely restore standard WordPress functionality when CR Guard is disabled or removed.
A deliberate security model
WordPress cannot be made safe by a single switch. CR Guard helps reduce common pathways by combining identity checks, privilege control, detection and fast visibility into sensitive change.
See the implementation approachCR Guard policy engine
Site-wide protection layer
Advanced security operations
CR Guard goes beyond detection with controlled review, remediation and recovery workflows for complex WordPress security operations.
Require authenticator verification for selected managed users, with recovery codes and owner-controlled resets.
Review, approve or revoke plugin and theme trust across multiple extensions in one controlled workflow.
Run dedicated scans for supported Portable SC payloads, loaders, recovery files and persistence indicators.
Quarantine selected confirmed threats with recovery records and optionally re-quarantine known returning content.
Review suspicious directives in .htaccess and .user.ini, then apply selective repair with recovery copies.
Inspect flagged JavaScript and proposed database changes before cleanup, with protected rollback data.
Search scheduled events and pause, resume or delete selected tasks when investigating persistence.
Filter executable uploads and supported SQL/PHP injection patterns with monitoring mode and configurable exceptions.
Questions, answered
Straight answers about what CR Guard protects, how it operates and where infrastructure security still matters.
Security guidance
Clear, practical answers
CR Guard is a WordPress application-security control plane for identity, API policy, malware and integrity checks, file monitoring, pre-execution trust, persistence defense and incident response.
No. It strengthens the WordPress boundary, but it works alongside WAF or CrowdSec protection, operating-system updates, tested backups, locked-down SSH/SFTP, safe filesystem ownership and database security.
Magic Link tokens are one-time and time-limited. The protected owner chooses the authentication mode, and the site should test WordPress mail delivery before relying on login or alert emails.
CR Guard governs managed identities and privileged actions instead of deleting WordPress users outright. This preserves a documented break-glass recovery path while reducing unmanaged account creation and privilege drift.
WordPress hooks can observe managed uploads immediately, while Rapid Watch, scheduled checks and deep SHA-256 verification detect broader content drift. True sub-second filesystem events require a persistent server agent.
Use the Incident Center to preserve evidence, assess severity, revoke affected sessions, run malware and persistence scans, review file history and only rebuild trusted baselines after cleanup is verified.
Yes. You can connect and use your own email delivery provider, such as SendGrid or another supported SMTP/email service. You only pay a $10/year platform fee for using your own email provider. There are no additional email delivery charges from the platform.